Secure Code & Remediation Training
Practical security training for developers, built around how real attacks work and the vulnerabilities in your own code.
Developers fix vulnerabilities faster, and introduce fewer of them, when they understand how attackers exploit them. Our secure code training is taught by the consultants who carry out our penetration tests, so it is grounded in the flaws we find in real applications every day.
We also run remediation training: focused sessions that take your team through the findings from a penetration test or code review, explain the root cause of each one and show how to fix it properly, so the same issues don't come back in the next release.
What Is Secure Code Training?
Secure code training teaches developers to recognise and prevent security vulnerabilities while they write code. Rather than a list of rules, our training shows how common weaknesses are found and exploited, then how to design and code them out, in the languages and frameworks your team uses.
Training can be tailored to web applications, APIs or mobile apps, and to your own technology stack and risks.
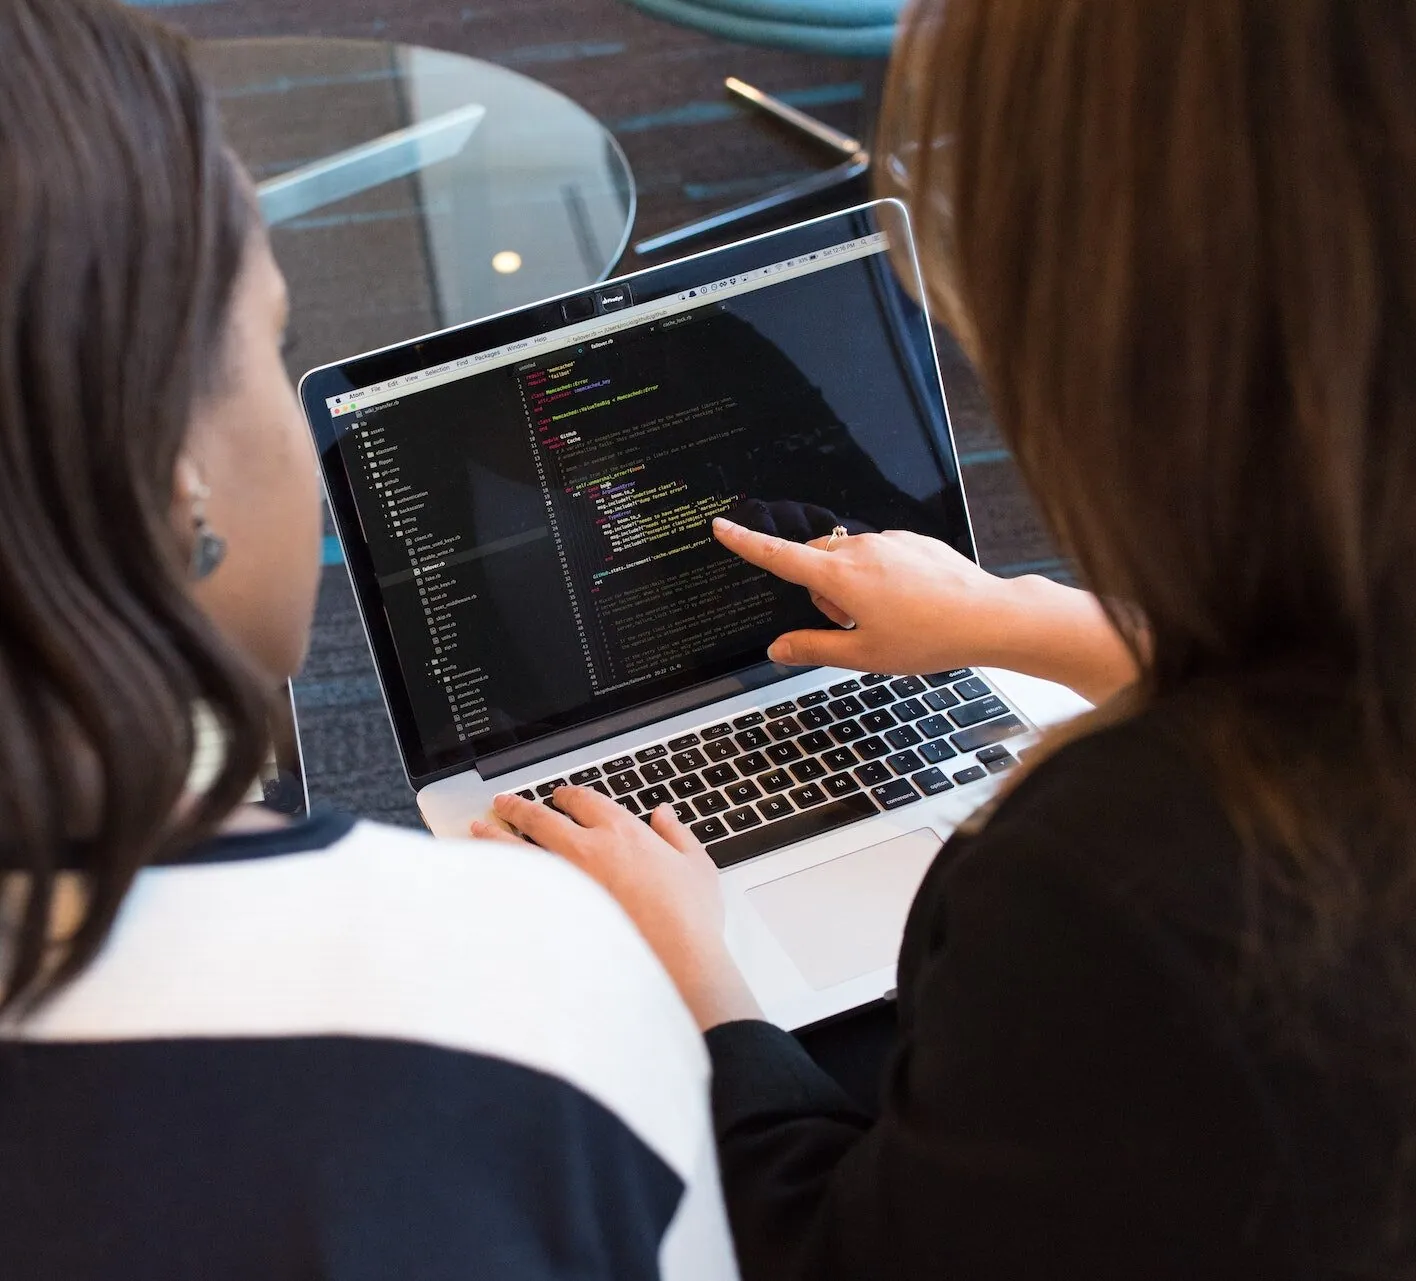
Why Train Your Developers?
Most application vulnerabilities come from a small number of recurring mistakes: missing authorisation checks, trusting user input, weak session handling, exposed secrets and vulnerable dependencies. Fixing them after a penetration test is slower and costlier than avoiding them in the first place.
Training gives developers the knowledge to prevent those mistakes, makes code review and security tooling more effective, and builds a culture where security is part of good engineering. It also provides evidence of secure development practice for customers, auditors and frameworks that ask for it.
What the Training Covers
How attackers think
Live demonstrations of how vulnerabilities are discovered and exploited, so developers see the impact of insecure code for themselves.
OWASP Top 10 and OWASP API Security Top 10
The most common and serious web application and API weaknesses, including broken access control, injection, authentication failures and security misconfiguration.
Secure design and coding practices
Input validation and output encoding, authentication and session management, authorisation patterns, cryptography, secrets handling and safe error handling.
Dependencies and the pipeline
Managing third-party libraries, and using security tooling such as static analysis and dependency scanning in your CI/CD pipeline.
Secure use of AI in development
Risks to watch for when using AI coding assistants, and how to build applications that use large language models safely.
Remediation workshops
Sessions built around the findings from your own penetration tests or code reviews, covering root causes, fixes and how to prevent similar issues.
Our Approach
01
Training needs
We talk to you about your team, languages, frameworks and the issues you want to address, including findings from previous tests.
02
Tailored content
We tailor the course content and examples to your stack and agree the format, length and audience with you.
03
Delivery
Our consultants deliver the training with demonstrations, examples and time for questions.
04
Follow-up
We can follow up with secure code review, testing of new releases or retesting of fixed findings to confirm the training is paying off.
Why Choose Samurai Security?
Taught by penetration testers
Our trainers are working CREST-accredited penetration testers, not presenters reading slides, so the content reflects real-world attacks.
01
Built around your code
We can use your own test findings and technology stack, so the training is immediately relevant to your developers.
02
Linked to testing
Training, code review and penetration testing from one team means lessons from testing feed straight into how your developers write code.
03
Our Work

Strengthening Cybersecurity Resilience
“Samurai takes the time to understand our needs and helps us to be an enabler for Flagship Group’s mission. It’s always a pleasure to work with them and I’d recommend them to others.”
Enabling Remote Work for the NHS
“When I have a problem nobody else can solve, I call Samurai because I know that they’ll deliver what I need, every time, without fail.”
Incident Response Retainers To Enable Growth
“This partnership has allowed us to scale and grow with the confidence that we are protected from cyber threats around the clock.”
Client Testimonials
“Samurai takes the time to understand our needs and helps us to be an enabler for Flagship Group’s mission. It’s always a pleasure to work with them and I’d recommend them to others.”
“We were astonished by what Samurai’s Black Dragon assessment revealed, even though we thought we had everything covered. The findings spoke for themselves, and the team’s expertise and clarity were outstanding.”

"Samurai’s Black Dragon: Attack Surface Risk Assessment was exactly what we needed and something we’ve never seen done before. They turned it around quickly, highlighted risks that could have easily been overlooked, and gave us a clear roadmap for improvement."
Frequently Asked Questions
Who is secure code training for?
Software developers, technical leads, testers and DevOps engineers who build or maintain web applications, APIs or mobile apps.
Can the training be tailored to our languages and frameworks?
Yes. We tailor examples and exercises to the languages, frameworks and platforms your team uses, and to the issues found in your own testing.
What is remediation training?
Remediation training is a focused session built around the findings from your penetration test or code review. We explain why each issue occurred, how to fix it properly and how to stop similar issues appearing again.
Do you also offer general cyber awareness training?
Yes. Our cyber security awareness training is designed for all staff, including phishing awareness and simulations, while secure code training is for your technical teams.
Related Services
DevSecOps & Secure Development
Secure code review, CI/CD pipeline security reviews and testing that fits your release cycle.
Web Application Penetration Testing
CREST-accredited testing of your web applications.
Cyber Security Awareness Training
Security awareness and phishing training for all staff.
CREST Training
Ethical hacking training that prepares candidates for the CREST Registered Tester exam.
Help your developers write secure code
Tell us about your team and we'll tailor a course that fits. Call us on 0114 400 0021 or get in touch online.
CTA label: Contact Us
Get in touch
Let's find a solution
If you want to chat, give us a call: 0114 400 0021
Or, email us: info@samuraisecurity.co.uk